GRCFlowAI-native GRC
Prove it. Own it. Quantify it. Attest it.
- Self-hosted
- A2A attestation
- Air-gap ready
- No telemetry
Prove it. Own it. Quantify it. Attest it.
AI-native compliance automation for teams that need verifiable control evidence, self-hosted deployment, auditor-ready proof, and peer-to-peer attestation.
Prove it — tamper-evident audit trail
Defend every number in an audit without asking anyone to take your word for it. Every verdict, evidence action and policy edit becomes a tamper-evident, cryptographically signed record — one an auditor can recompute from scratch to confirm nothing was changed.
Learn more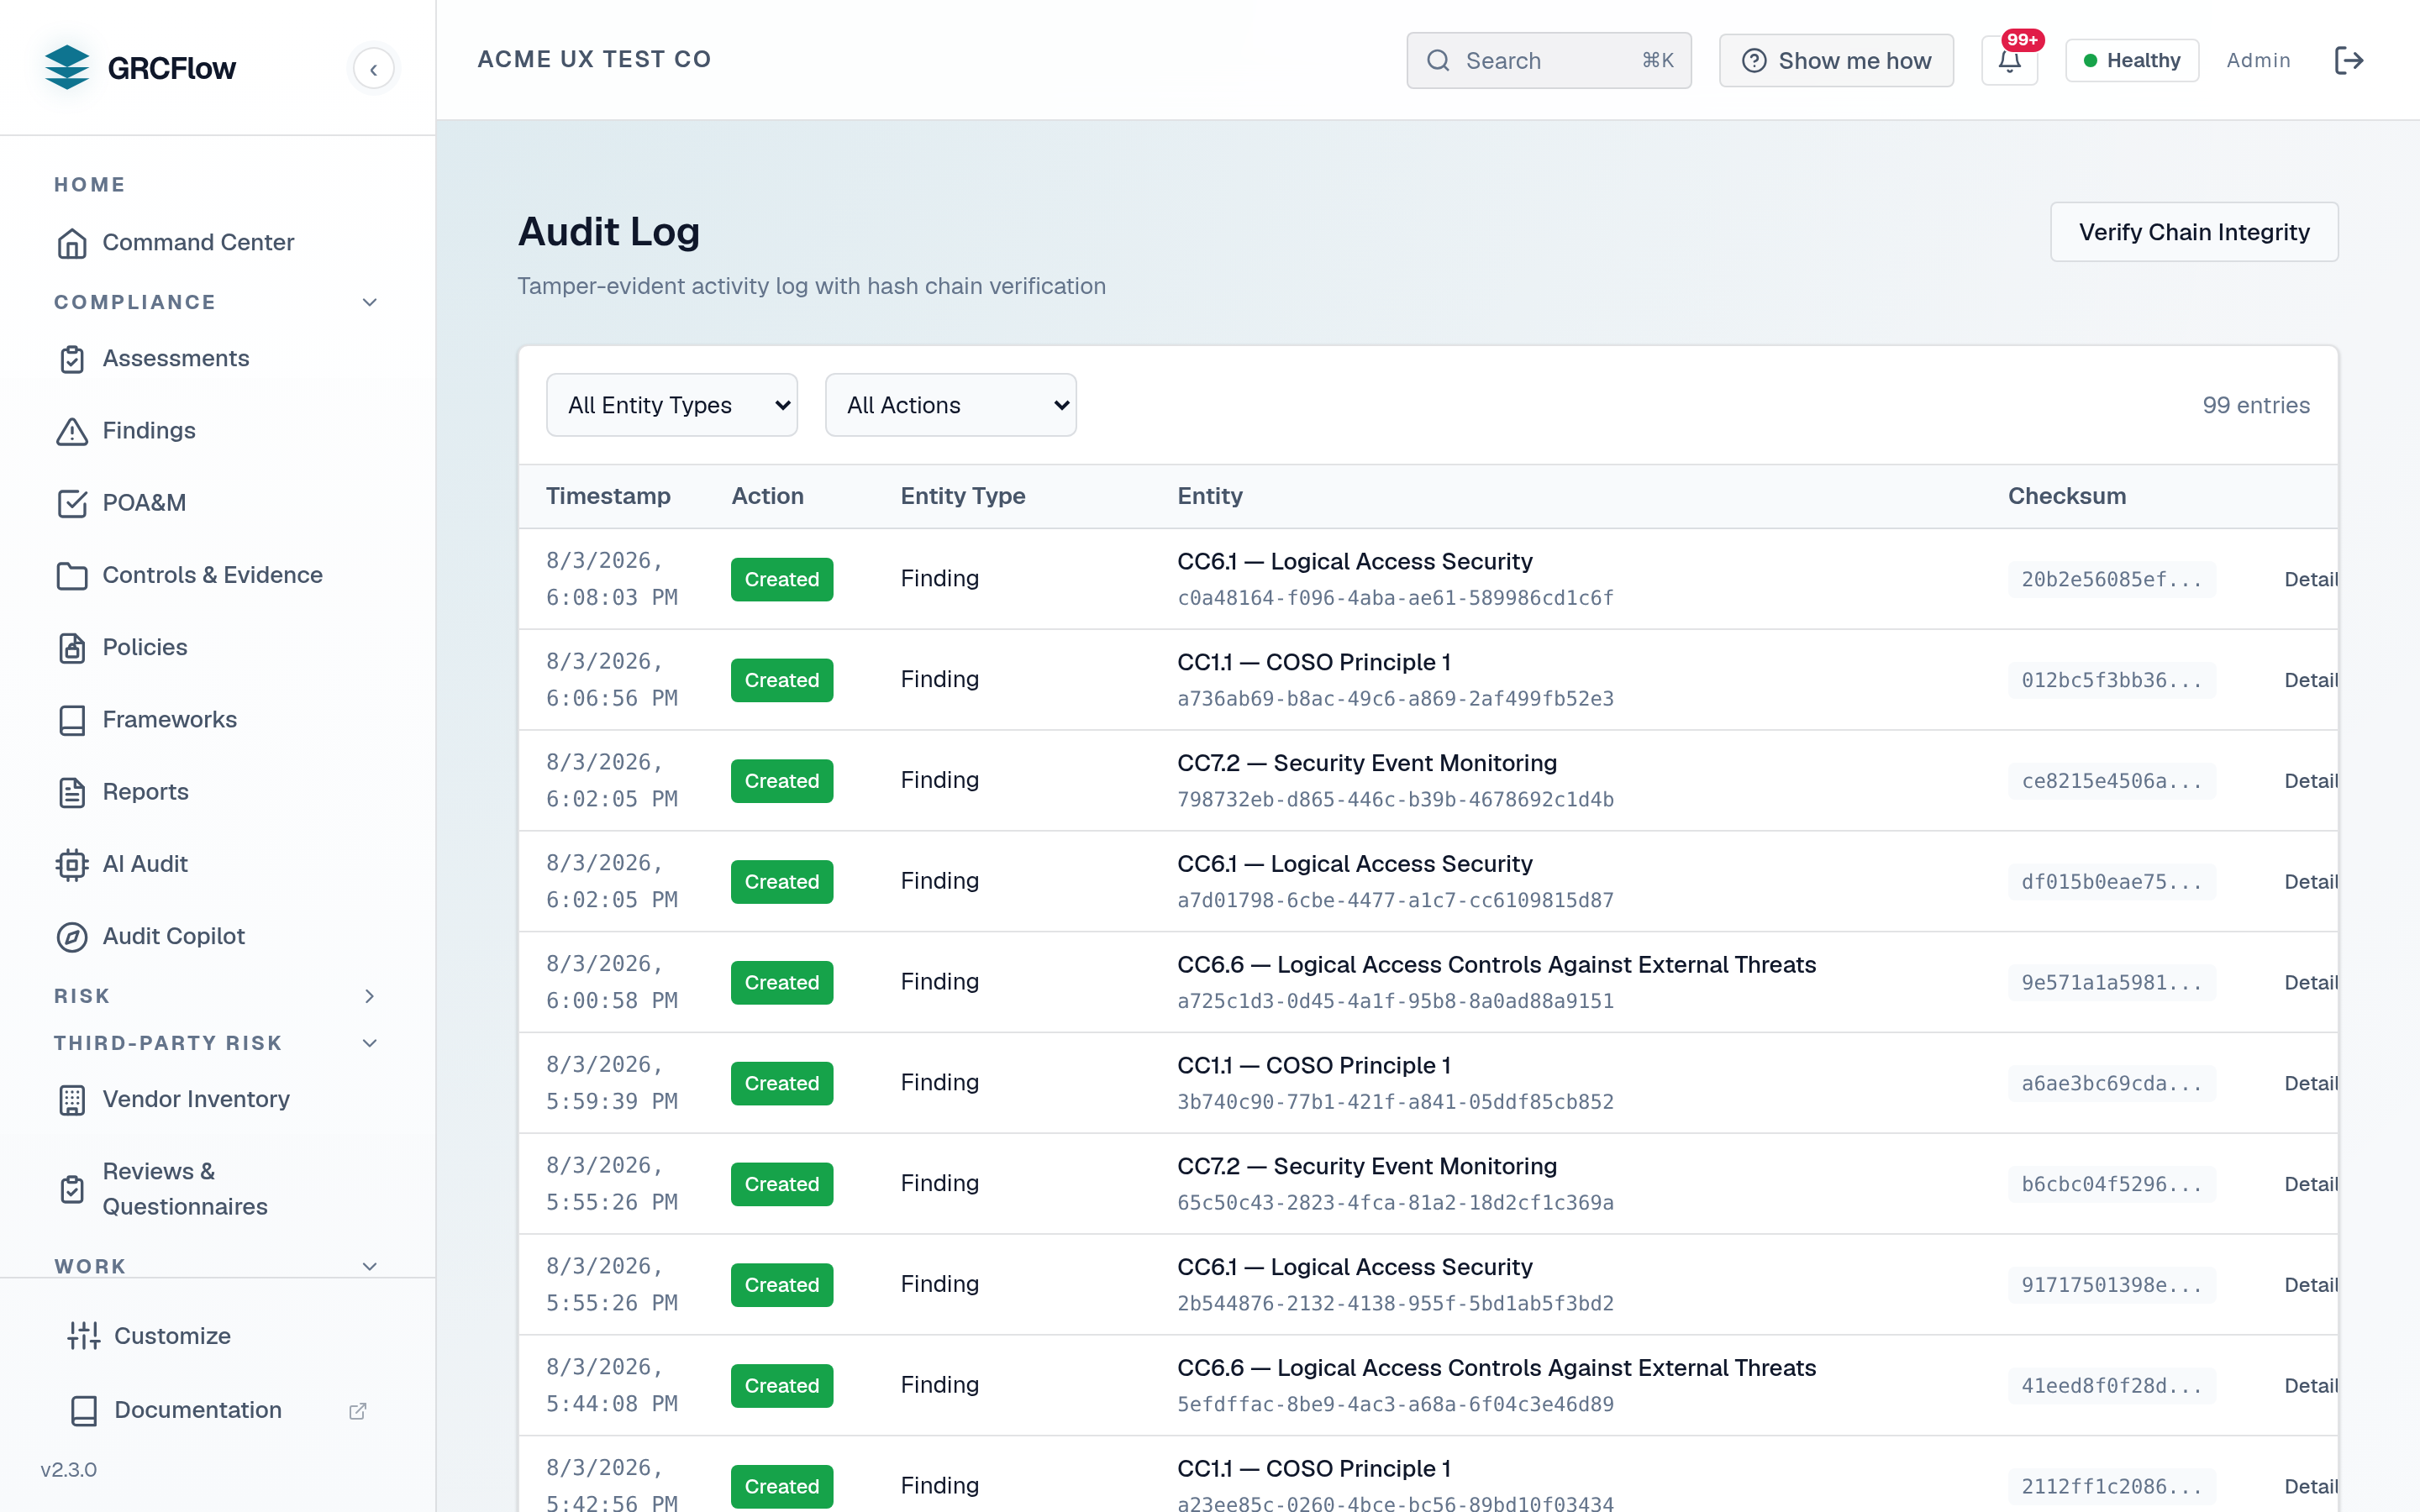
Own it — self-hosted, no lock-in
No vendor holds your data hostage. It runs entirely on your own infrastructure, air-gap capable — and if you stop paying, your instance goes read-only while you keep full read and export access.
Learn more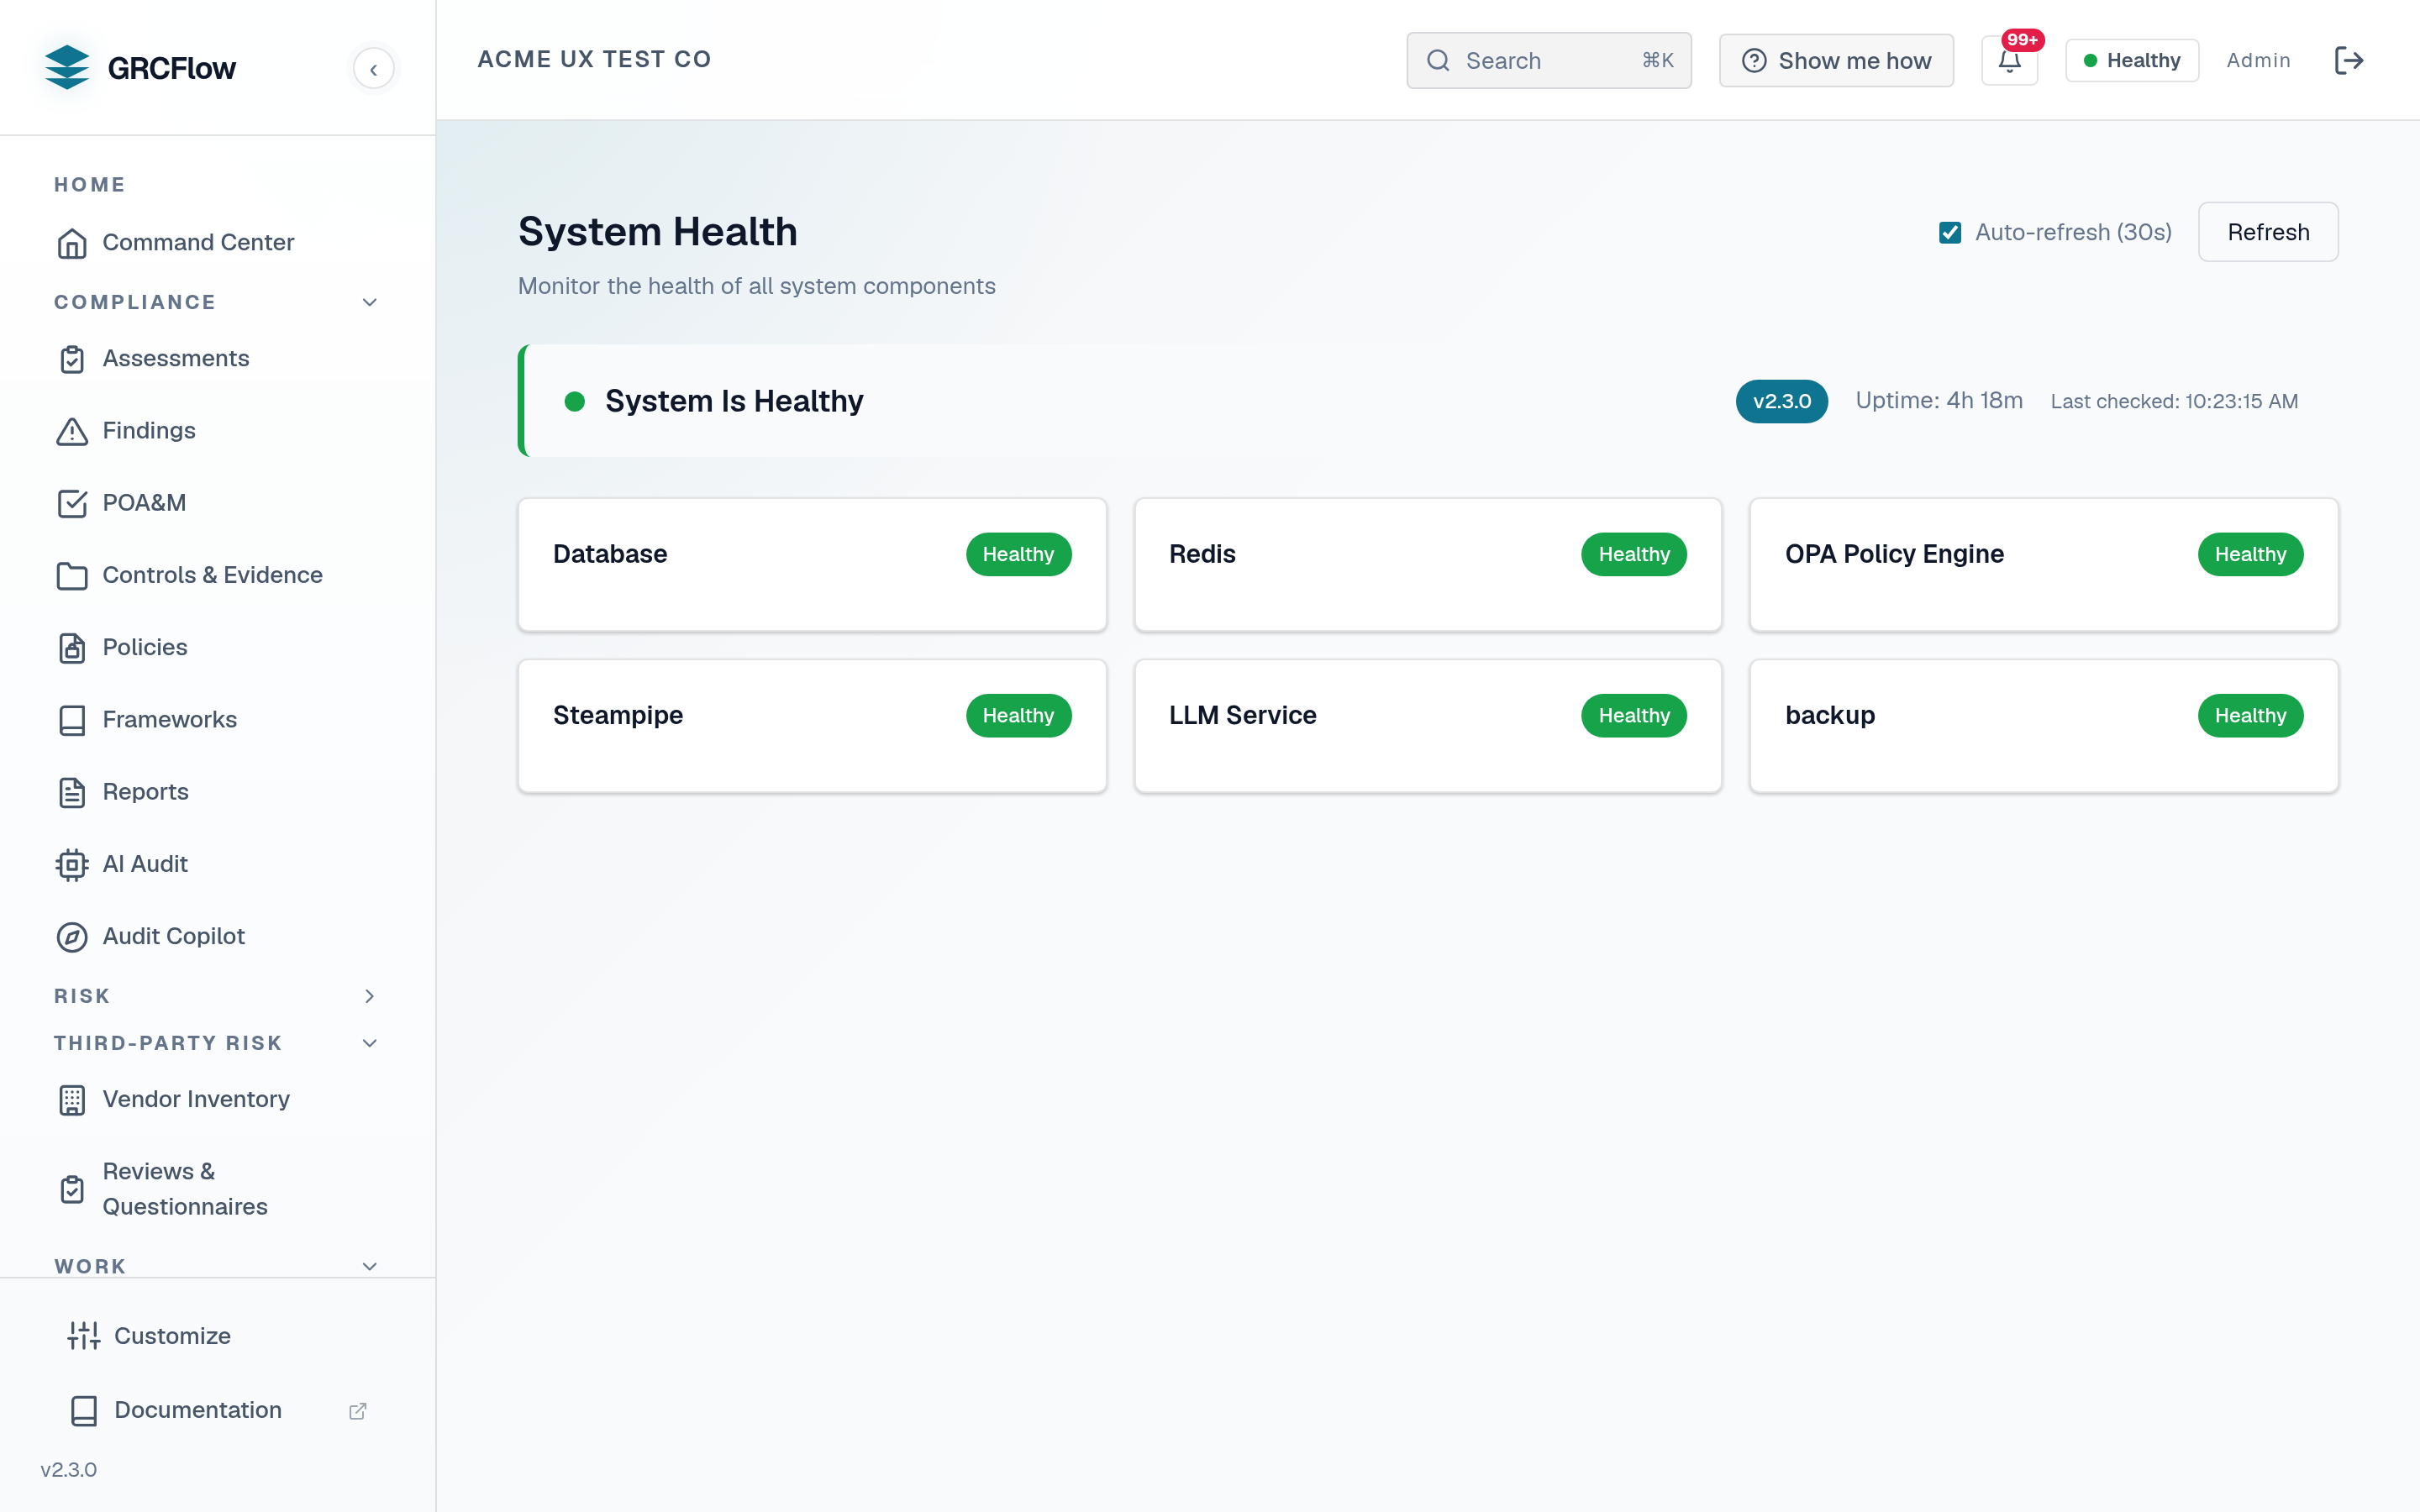
Quantify it — risk in dollars
See risk as a dollar figure your board and CFO can act on — annual expected loss, with a likely-to-worst-case range and every assumption shown. It’s built on the Open FAIR standard, so the numbers can be challenged, not taken on faith.
Learn more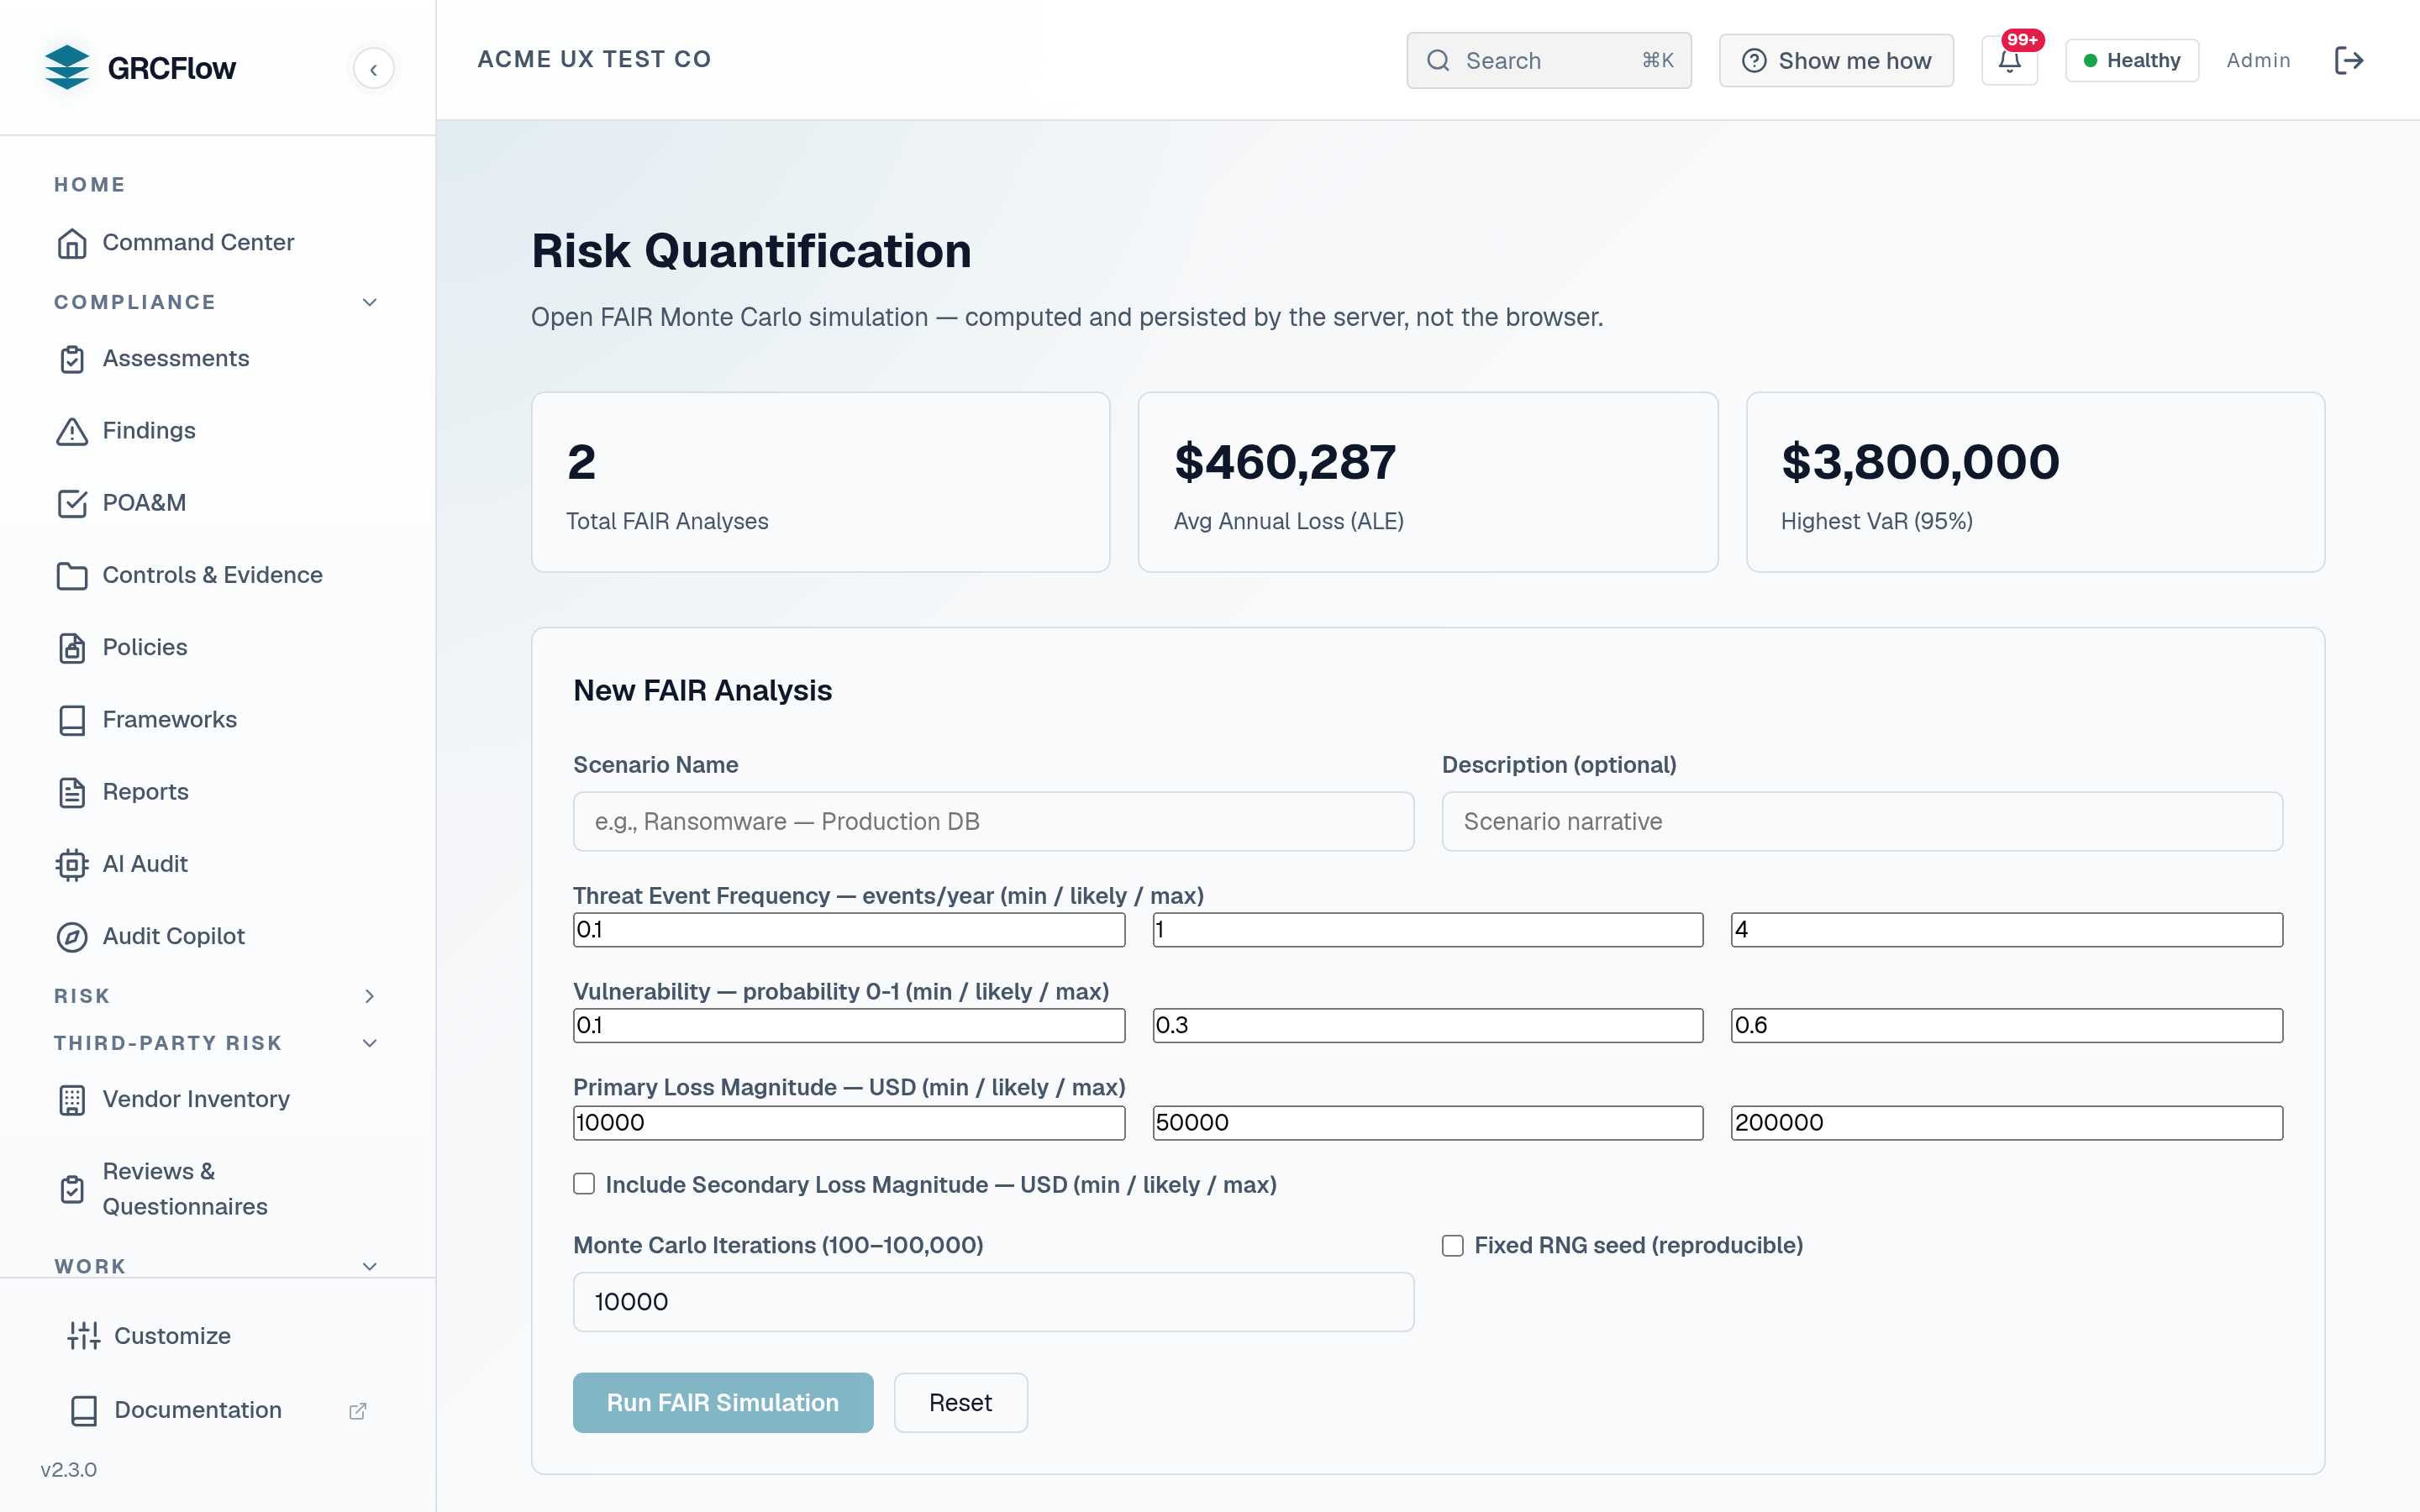
Attest it — signed proof, on demand
When a partner or customer needs to verify your control posture, their system can query yours directly and get back a signed, current answer. It’s recomputed from your latest completed assessment on every request, valid 30 days, and verifiable offline.
Learn more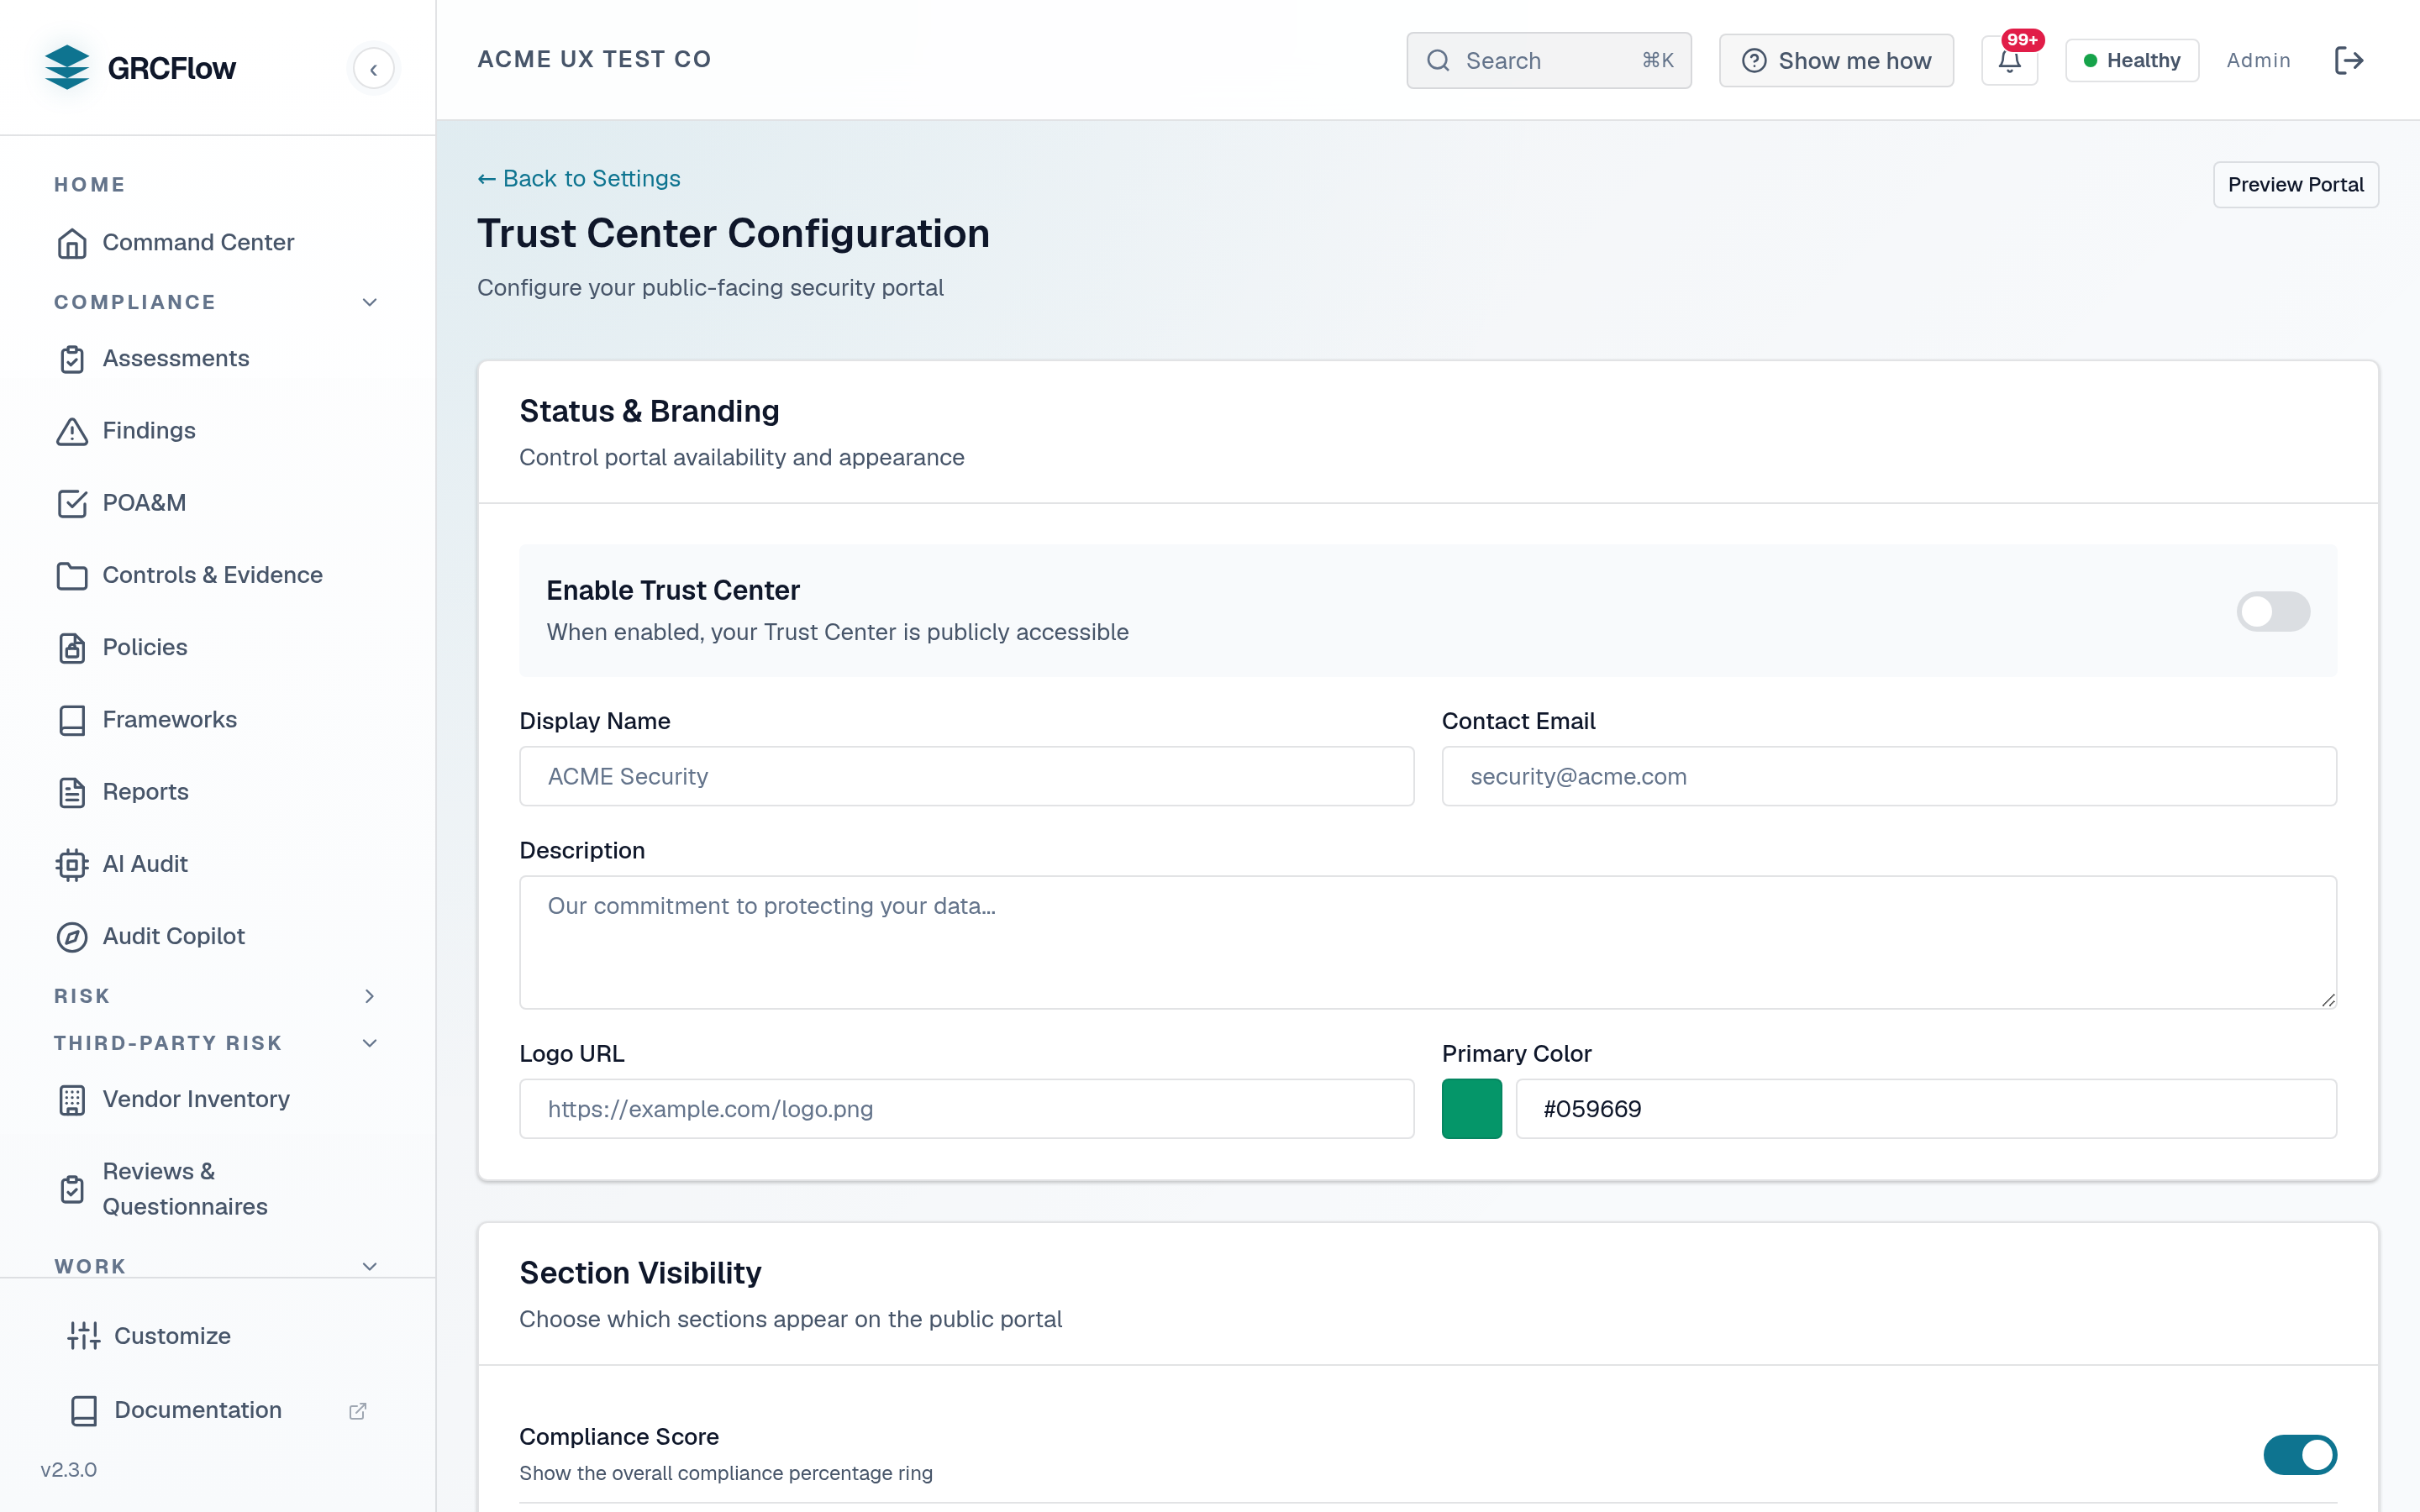

Prove your posture to partners, live and signed
A parent company, prime or bank queries your instance and gets back a signed attestation they can re-check any day. No shared cloud tenant.
How continuous attestation works